What vpns on github really mean and how to use them safely

What vpns on github really mean and how to use them safely: a practical guide to understanding VPN repos, what they do, and how you can protect yourself when exploring or using them.
Quick fact: VPNs on GitHub can be legitimate tools or risky projects, so you should verify the source, read the code, and follow best safety practices before using or distributing anything related to VPNs.
If you’re here, you probably want to know how to navigate VPN-related repositories on GitHub safely. Here’s a concise guide that breaks down what these projects are, how they work, and a step-by-step approach to using them responsibly. Think of this as a friendly roadmap you can follow start to finish. Nordvpn on your iphone in china your step by step guide to staying connected
- What you’ll learn in this guide:
- How to identify trustworthy VPN repositories
- Key terms and concepts you’ll encounter
- Safety steps before running VPN software from GitHub
- How to audit code quickly, plus common red flags
- A quick checklist for safe usage and maintenance
Useful resources to have on hand text-only URLs: Apple Website - apple.com, GitHub Documentation - github.com, OpenVPN Project - openvpn.net, WireGuard - www.wireguard.com, Linux Foundation - linuxfoundation.org, Reddit VPN subreddit - www.reddit.com/r/VPN, Wikipedia VPN - en.wikipedia.org/wiki/Virtual_private_network, GitHub Security - github.com/security, Privacy guides - www.eff.org/deeplinks/ostatic, Tor Project - www.torproject.org
Introduction: what vpns on github really mean and how to use them safely What vpns on github really mean and how to use them safely: on GitHub, VPN-related projects range from official clients and open-source protocols to experimental tools and misconfigured scripts. The key is to separate the signal from the noise. In this guide, you’ll find a practical, action-oriented approach to evaluating, using, and maintaining VPN software sourced from GitHub.
- Quick-start checklist:
- Verify the repository’s legitimacy maintainer credibility, fork activity, issues response.
- Check the license and contribution guidelines.
- Review recent commits for security-minded changes.
- Read the README for installation and usage specifics.
- Inspect the code you’re going to run, or use prebuilt binaries from trusted sources.
- Run in a controlled environment first virtual machine or container.
- Monitor network activity and logs after deployment.
- Keep the software up to date with security patches.
In this article, you’ll find a structured, human-friendly breakdown with practical steps, real-world examples, and safety tips. We’ll cover definitions, risk factors, verification steps, usage patterns, and a clearly labeled FAQ so you can quickly find answers when you’re in a pinch.
What a VPN repo on GitHub typically includes
Core components you’ll encounter: Turbo vpn edge extension review for microsoft edge users in 2026: fast, private, and practical for Edge fans
- Client applications that configure and connect to VPN servers
- Protocol implementations e.g., OpenVPN, WireGuard and client tooling
- Scripts for deployment, testing, or automation
- Documentation, examples, and configuration templates
- CI/CD pipelines and security tests
Common file types you’ll see:
- README.md with installation steps and usage notes
- LICENSE files outlining how you can use the code
- go, rust, c, python source files depending on the project
- Dockerfile and docker-compose.yml for containerized setups
- Kubernetes manifests for deploying VPN services
- shell scripts .sh, PowerShell scripts .ps1
- config files .ovpn for OpenVPN, .conf for WireGuard
- tests and review notes in tests/ or .github/workflows
Why VPN repos on GitHub can be risky and how to mitigate
Risks to watch for:
- Malicious code or backdoors sneaking into builds
- Exposed credentials hard-coded tokens, keys, or secrets
- Outdated or deprecated security protocols
- Insecure default configurations that leak data
- Poorly documented dependencies or supply chain risks
How to mitigate:
- Favor repos with strong maintenance activity and clear security practices
- Look for a responsible disclosure policy and recent security advisories
- Validate the code locally before connecting to any network
- Use signed releases or verified builds where possible
- Isolate VPN usage to test environments first
Step-by-step: evaluating a VPN repository on GitHub Zenmate vpn what it was why it disappeared and what you need to know now
Step 1: assess the repo’s authority
- Check the owner organization vs. individual
- Review the number of stars, forks, and issues
- See if there’s a dedicated security or maintainers team
Step 2: read the documentation
- Look for setup instructions, prerequisites, and supported platforms
- Verify whether the project supports your OS and device type
- Confirm whether there are instructions for auditing or customizing security settings
Step 3: examine the code excerpts
- Scan for hard-coded secrets, exposed endpoints, or insecure defaults
- Look at how credentials are handled environment variables vs. files
- Check for dependency management and use of verified packages
Step 4: review the commit history
- Are there frequent commits addressing security or bug fixes?
- Do pull requests have meaningful discussions and code reviews?
Step 5: run in a safe environment Why Your vpn isnt working with mobile data and how to fix it
- Build in a sandbox VM or container and avoid exposing personal data
- Test basic connectivity, DNS privacy, and leak tests
- Verify the VPN’s DNS resolution, split tunneling, and kill-switch behavior
Step 6: verify the trust signals
- Digital signatures for releases
- CI checks that include security tests
- Community engagement in issues and responses
Important safety patterns when using GitHub VPN projects
- Prefer official repositories or widely trusted communities
- Use release binaries rather than building from source when possible
- Use containerized deployments to minimize host system changes
- Always test in a controlled environment before moving to production
- Maintain an incident response plan if you suspect a compromise
Case study: running a reputable OpenVPN client from GitHub
What to look for:
- An active, well-documented project with clear build steps
- A stable release channel with signed binaries
- Simple, minimal default configurations with explicit security settings
Quick setup example: Supernet vpn vs nordvpn why one isnt an option anymore and what to use instead
- Clone the repo from a trusted maintainer
- Review the README for prerequisites OpenSSL, TLS libraries, kernel modules
- Build or install the client via official packages
- Generate or import a configuration file from your VPN provider
- Connect and verify the tunnel with a leak test DNS, IPv6, and WebRTC checks
Post-setup checks:
- Confirm the VPN interface is up e.g., tun0 or similar
- Run a connectivity test to ensure traffic routes through the VPN
- Verify that your real IP address is masked and DNS requests are resolved via the VPN
Security best practices for VPN plugins and scripts on GitHub
- Use versioned releases, not raw branches, to minimize surprises
- Limit permissions to what’s strictly necessary least privilege
- Keep sensitive data out of source control use environment variables or secret management
- Watch for deprecated or vulnerable dependencies and patch promptly
- Regularly audit dependencies with security scanners or SCA tools
What to do if you suspect something is off
- If you see suspicious behavior, stop using the repo, and report it
- Check for existing advisories or disclosures from the maintainers
- Consider forking and patching the issue yourself if you have the know-how
- Notify your network or security team if you’re in a managed environment
Use cases: when to consider VPN repos from GitHub
- When you need a custom VPN client tailored to a specific setup
- When you want to contribute to open-source VPN projects
- When you’re learning about VPN protocols and want hands-on practice
- When you’re evaluating open-source options before choosing a commercial VPN
Red flags to avoid Unlock tiktok globally the vpns that actually work in 2026: The Essential Guide to Access TikTok Anywhere in 2026
- Projects with minimal documentation and no activity history
- Repositories with frequent sensitive data exposure in issues or commits
- Absent or vague security policies and no clear attribution or testing
- Unverified builds or unsigned release artifacts
Best practices for teams using GitHub VPN projects
- Establish a security policy for open-source component usage
- Use a software bill of materials SBOM to track dependencies
- Implement code review workflows focusing on security implications
- Create a sandbox environment for testing before deployment
- Keep an incident response plan and run drills
Comparison: VPN implementations you might find on GitHub
- OpenVPN clients and tooling
- Pros: Strong, proven protocol; wide compatibility
- Cons: Sometimes more complex to configure
- WireGuard-based clients
- Pros: Simplicity, performance, modern crypto
- Cons: Compatibility may vary across platforms
- Custom VPN scripts and automation
- Pros: Quick deployment and automation
- Cons: Higher risk if scripts aren’t well-audited
- Kubernetes VPN solutions
- Pros: Scales well; good for teams and clusters
- Cons: More complex to secure cluster networking
Table: quick decision matrix for choosing a GitHub VPN project
- Criteria: Maintenance activity, Security posture, Documentation, Build process, Platform support, Community engagement
- Scoring: 1-5 scale higher is better
- Example: A repo with 4 for maintenance, 5 for security, 4 for docs, 3 for build, 5 for platform support, 4 for community gets a strong overall score
Enhancing trust: how to contribute responsibly
- If you contribute, start with small, well-scoped changes
- Follow the project’s contribution guidelines
- Improve documentation where possible
- Report security concerns through the proper channels
- Share test results and proof of concepts responsibly
Practical tips for readers Openvpn Not Working On Windows 11 Heres How To Fix It Fast: Quick Fixes For Common Issues And Setup Tips
- Always verify the source before downloading anything from GitHub
- Use a separate device or VM for testing VPN software
- Keep your host OS and dependencies up to date
- Avoid exposing sensitive credentials or tokens in config files
- Document your steps so others can reproduce safely
Frequently Asked Questions
What are VPNs on GitHub?
VPNs on GitHub are projects that implement, extend, or automate Virtual Private Network functionality. They can be official clients, protocol implementations, deployment tools, or experimental projects. Always verify trust and security before using them.
How can I tell if a VPN repo is trustworthy?
Check the maintainer’s credibility, recent activity, issue response times, the presence of a security policy, signed releases, and a transparent history of code reviews.
Should I download binaries from GitHub for a VPN client?
If possible, use official releases from trusted maintainers or verified builds. Binaries from unknown sources can be risky. Prefer building from source only if you trust the process and have security checks.
What is a kill switch in a VPN, and why does it matter?
A kill switch ensures that if the VPN disconnects, your traffic doesn’t leak outside the tunnel. It’s a critical security feature, especially for privacy-conscious users. Gm vpn login Your Step by Step Guide to Accessing GMS Network: Quick Start, Tips, and Best Practices
How do I test a VPN connection for leaks?
Test for IP leaks, DNS leaks, and WebRTC leaks. You can use online tools and command-line utilities to confirm that your public IP and DNS queries are routed through the VPN.
Can VPN software from GitHub impact my device’s security?
Yes. Poorly maintained or poorly coded VPN software can introduce vulnerabilities, data leakage, or system instability. Always vet and isolate before production use.
What if I find a security vulnerability in a GitHub VPN repo?
Follow responsible disclosure guidelines. Contact the maintainers privately, provide details, and give them time to respond before making information public.
Do VPN projects on GitHub support all operating systems?
Not always. Support varies; some projects focus on Linux, others support Windows, macOS, or mobile platforms. Check the repository’s docs for platform specifics.
How do I keep VPN software from GitHub secure over time?
Regularly update to the latest releases, follow security advisories, monitor for new vulnerabilities, and implement robust configuration and patch management processes. Unlock anything online your guide to using expressvpn for unblocking and beyond
Should I contribute to VPN projects on GitHub?
If you have skills in security, networking, or software development, contributing is a great way to help. Start by fixing small issues, improving tests, or enhancing documentation.
Conclusion What vpns on github really mean and how to use them safely can be summed up in a few practical ideas: verify, test in isolation, review, and stay aware of security practices. By following the steps outlined in this guide, you can explore VPN-related GitHub projects with greater confidence and minimize risk while learning or building exactly what you need.
| VPN | Obfuscation | From / month | Plan | Free plan | Refund | Alipay | UnionPay | Crypto | Website opens in China | Trustpilot | |
|---|---|---|---|---|---|---|---|---|---|---|---|
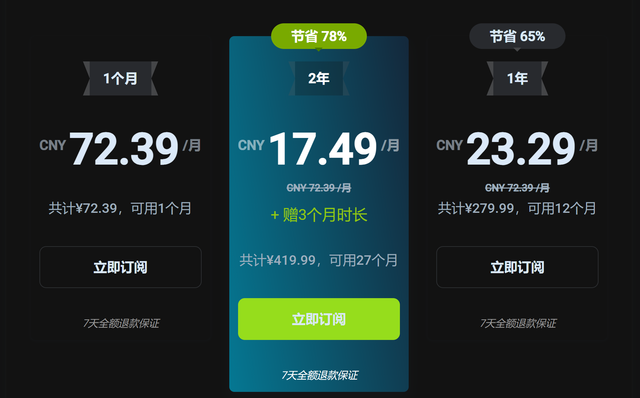
 ZoogVPN | Turn on manually Shadow | $2.49/mo | 27 months: $59.99 | Yes | 7 days | ✓ | ✓ | ✓ | ✓ | Official site blocked; our special link opens (4.4 s) | 4.2/5 (195 reviews) |
 NordVPN | Turn on manually Obfuscated Servers / NordWhisper | $3.49/mo | 27 months: $94.23 | No | 30 days | ? | ✗ | ✓ | ✓ | ✗ Blocked | 4.2/5 (51,628 reviews) |
 ExpressVPN | ✓ On by default all servers | $3.00/mo | 28 months: $84 | No | 30 days | ✗ | ✗ | ✓ | ✗ | ✗ Blocked | 4.4/5 (29,706 reviews) |
 Surfshark | ✓ On by default Camouflage, with OpenVPN | See site | See site | No | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.3/5 (31,823 reviews) |
 Proton VPN | Turn on manually Stealth, free plan too | $2.99/mo | 12 months: $35.88 | Yes | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 2.1/5 (1,040 reviews) |
 Astrill VPN | Turn on manually StealthVPN / OpenWeb | $12.50/mo | 24 months: $300 | No | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 1.3/5 (110 reviews) |
 Private Internet Access | Turn on manually Shadowsocks, OpenVPN only | $2.03/mo | 40 months: $81.2 | No | 30 days | ✗ | ✗ | ✗ | ✗ | ✗ Blocked | 4.2/5 (11,033 reviews) |
 CyberGhost | Turn on manually selected servers | $2.19/mo | 28 months: $61.32 | No | 45 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.0/5 (24,178 reviews) |
 PureVPN | Turn on manually switch to OpenVPN | $1.69/mo | 60 months: $101.55 | No | 31 days | ? | ? | ✗ | ✓ | ✗ Blocked | 4.4/5 (17,994 reviews) |
 AdGuard VPN | ✓ On by default TrustTunnel | $2.99/mo | 24 months: $71.76 | Yes | 30 days | ✓ | ✗ | ✓ | ✓ | Official site blocked; our special link opens (3.7 s) | 4.3/5 (290 reviews) |
 Mullvad | Turn on manually QUIC / Shadowsocks / LWO | $5.61/mo | €5/mo | No | 14 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 3.2/5 (192 reviews) |
 Windscribe | Turn on manually Stealth / WStunnel | $5.75/mo | 12 months: $69 | Yes | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.7/5 (13,355 reviews) |
 StrongVPN | Turn on manually Scramble, OpenVPN TCP | See site | See site | No | 30 days | ✓ | ✗ | ✗ | ✗ | ✗ Blocked | 4.4/5 (2,695 reviews) |
 LightXtreme 闪连 | Not listed | $7.08/mo | 12 months: $84.99 | Yes | 30 days | ✓ | ✓ | ✓ | ✓ | ✓ Yes (3.5 s) | No page |
Prices checked 2026-11-10 on each vendor's pricing page (cheapest long plan, USD). Check the vendor's checkout for the final price.
Obfuscation checked 2026-11-14 on each vendor's site and help center: "on by default" = nothing to set; "turn on manually" = switch protocol or mode in settings; "not listed" = the vendor describes no obfuscation.
Payment methods checked 2026-11-10 on each vendor's payment pages: all 14 take cards and PayPal; ✗ = not listed, ? = the vendor's own pages disagree.
China access: whether the official website opens from mainland China networks (tests the website only, not the VPN connection). Last checked 2026-11-18 01:02 Beijing time.
Trustpilot score and review count checked 2026-11-10.